Defending Authentication Tokens During Prozone Login and Isolating Sandboxed Sessions on the Prozone CC Marketplace
Modern web tracking mechanisms have evolved far beyond basic HTTP tracking cookies. When operators interact with prozone.cc, commercial analytics networks and adversarial sniffers attempt to construct persistent device identifiers using passive hardware rendering quirks. Establishing robust browser isolation ensures that account credentials and transactional queries remain strictly sandboxed from outside surveillance.
Prior to initiating a sensitive prozone login session on the authentic prozone official website, security researchers configure disposable client profiles that randomize canvas hashes, block WebRTC IP disclosures, and compartmentalize local storage. This technical guide details the configuration directives necessary to enforce zero-entropy anonymity.
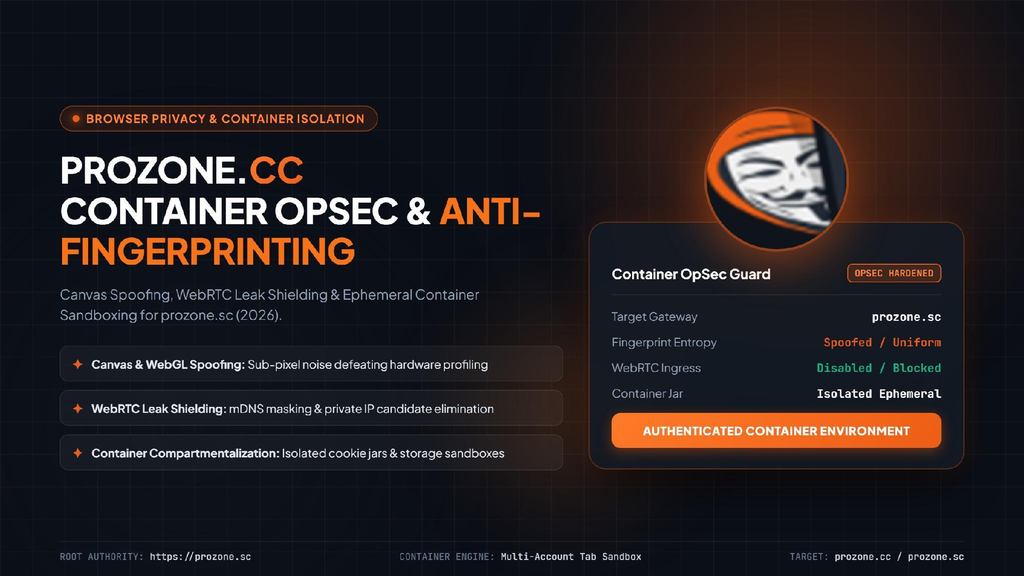
Figure 1: Prozone.CC Client Hardening Architecture: Canvas Noise Injection, WebRTC IP Shielding, and Ephemeral Container Isolation.
1. Advanced Device Fingerprinting Vectors: Canvas, WebGL & AudioContext Spoofing
Device fingerprinting scripts execute hidden HTML5 2D canvas instructions and query WebGL rendering buffers to extract unique microscopic hardware signatures. Because different GPU chipsets, display drivers, and anti-aliasing rasterizers render 3D geometry with sub-pixel variances, a single call to getImageData can generate a 32-bit hardware hash with over 18 bits of identifying entropy.
To counteract this vector, hardened browser profiles inject pseudo-randomized mathematical noise into RGB channel buffers on every read operation. This changes the calculated hash dynamically without breaking legitimate UI rendering elements. In parallel, WebGL unmasked vendor and renderer strings must be masked to generic values (e.g., standard Intel UHD Graphics or Mesa drivers).
| // Hardened user.js Preferences for Anti-Fingerprinting user_pref(“privacy.resistFingerprinting”, true); user_pref(“privacy.resistFingerprinting.letterboxing”, true); user_pref(“webgl.disabled”, false); user_pref(“webgl.override-unmasked-vendor”, “Intel Open Source Technology Center”); user_pref(“webgl.override-unmasked-renderer”, “Mesa DRI Intel(R) UHD Graphics 620”); user_pref(“dom.webaudio.enabled”, false); |
2. WebRTC IP Leak Mitigation & Encrypted Client Hello (ECH)
WebRTC (Web Real-Time Communication) introduces a severe security flaw through Interactive Connectivity Establishment (ICE) candidate enumeration. Even when routing network traffic through an encrypted proxy or VPN gateway, unshielded STUN requests can disclose the client’s actual private LAN address (e.g., 192.168.1.45) and true ISP WAN gateway.
When browsing catalog inventories on the prozone cc marketplace, operators must disable ICE candidate generation or force mDNS address masking. Combining this policy with Encrypted Client Hello (ECH) protects Server Name Indication (SNI) payloads during initial TLS handshakes, stopping upstream network eavesdroppers from identifying target destination endpoints.
| Isolation Profile | Canvas / WebGL Vector | WebRTC Leak Exposure | Entropy Resistance |
| Standard Chromium (Default) | Direct Hardware Readout | Full STUN Local/WAN IP Leak | Low (18.4 Bits Entropy) |
| Hardened Firefox Container | Sub-Pixel Noise Injection | mDNS Masking Enforced | High (5.2 Bits Uniform) |
| Brave Strict Shields | Randomized Per-Session Seed | Non-Proxied UDP Blocked | High (4.8 Bits Uniform) |
| Whonix / Tor Browser | Uniform Fixed Baseline | WebRTC Sockets Disabled | Maximum (0.0 Bits Entropy) |
3. Multi-Account Container Tabs & Sandboxed Ephemeral Workspaces
Session leakage occurs when browser tabs share global state variables such as localStorage, IndexedDB tables, shared service workers, and HTTP cache graphs. Containerization technology isolates these resources into independent contextual identities. Each container maintains a distinct cookie jar, isolating authenticated sessions from all adjacent web activities.
For optimal operational security, operators assign a dedicated, single-use container to each platform session. Upon concluding transactional tasks, closing the container tab instantly purges session tokens, ephemeral cookies, and cached artifacts from memory, ensuring zero cross-session correlation.
| Summary: OpSec Verification ChecklistBy hardening client parameters against canvas profiling and enforcing strict container isolation before authenticating through prozone.cc, users shield their digital identity, prevent IP leakage via WebRTC, and ensure total compartmentalization across all portal transactions. |
About Prozone.CC Network
The official prozone official website provides secure access gateways and privacy-hardened tools. Always verify genuine endpoints during prozone login and utilize sandboxed profiles on the prozone cc marketplace at prozone.sc.